The October Visa Bulletin Is Late. Here’s Why That Might Be OK.

The State Department has not yet published the October 2026 visa bulletin. The delay is running past its usual pattern. As of September 26, 2026, the department’s website still listed the October edition as “Coming Soon.” The September bulletin remained the current reference for green card applicants.

That gap matters because October marks the start of a new fiscal year. Annual visa number limits reset then for employment-based and family-sponsored categories. Applicants in backlogged categories, especially EB-2 India, watch this bulletin closely every year.

How late is the October 2026 visa bulletin, really

Recent October bulletins have typically carried document dates in early September. October 2025’s bulletin was dated September 3, and so was October 2024’s. October 2023’s came out September 8, according to a review by QueueCheck. This year’s bulletin is running well behind that pattern, and behind a related forecast from Shusterman.com.

The State Department has not given a public reason for the delay. QueueCheck’s reporting is careful not to assign a cause. It avoids blaming staffing, policy, demand, or any annual-limit calculation without an official statement.

Why the delay does not confirm a retrogression

A late bulletin naturally fuels speculation. A delay by itself does not signal bad news, though. QueueCheck’s analysis stresses that a later release “does not by itself signal a larger advance, a retrogression, or a particular USCIS filing-chart choice.” Applicants sometimes read timing as a signal. It may simply reflect internal review taking longer than usual.
Applicant handing a document across a counter, representing the wait for the October 2026 visa bulletin

Who is watching the October 2026 visa bulletin most closely

EB-2 India and EB-5 unreserved India applicants have the most riding on this release. Earlier bulletins had suggested a possible October advance for those categories, though only on a conditional basis. Family-sponsored applicants are also waiting. So are those filing adjustment-of-status paperwork, since USCIS issues a separate filing chart tied to the same fiscal year reset.

What happens once the bulletin finally appears

Applicants should wait for the official October table rather than relying on forecasts circulating online. Once it posts, adjustment-of-status filers still need to check USCIS’s own filing-chart announcement separately. The two documents do not always move in lockstep. Expect a wave of law-firm analysis within hours of the bulletin’s release, given how many applicants are waiting on it.

FAQ: the delayed bulletin

Why hasn’t the October 2026 visa bulletin been published yet?

The State Department has not given an official reason. As of September 26, 2026, its website still listed the bulletin as “Coming Soon,” later than the typical early-September release pattern.

Does a delayed bulletin mean priority dates will retrogress?

Not necessarily. Analysts reviewing the delay have said it does not by itself signal an advance, a retrogression, or a specific USCIS filing-chart decision.

Which visa categories are most affected by the delay?

EB-2 India and EB-5 unreserved India applicants are watched most closely, along with family-sponsored categories, since October marks the annual reset of visa number limits.

When do October visa bulletins usually come out?

Recent years show a pattern of early-September release dates: September 3 in both 2024 and 2025, and September 8 in 2023.

What should applicants do while they wait?

Wait for the official October table rather than relying on predictions, and check USCIS’s separate filing-chart announcement once it posts, since it can differ from the State Department bulletin.

Continue reading on Tamara News

For more visa and immigration news, see our coverage of the September 2026 visa bulletin, the new USCIS Form I-864 rejections, and Canada’s study permit proof-of-funds rule.

Italy’s September 30 Air Traffic Strike: What to Know

A four-hour nationwide air traffic control strike is set to hit Italy on September 30, 2026, running from 13:00 to 17:00 local time, with ENAV and its subsidiary Techno Sky both walking out and disruption expected at airports from Milan to Naples. For anyone flying in, out of, or over Italy that afternoon, the practical question is not whether there will be delays, but how much of the day’s schedule falls inside the strike window.

What’s actually happening

According to Strike Tracker’s rundown of the action, the walkout covers ENAV staff and Techno Sky personnel across the country, with specific action confirmed at Bari, Bologna, Milan Linate, ENAV’s Rome headquarters and Naples. Separately, AirportStrikes.eu’s listing for Bologna’s Guglielmo Marconi Airport confirms the same September 30, 13:00-17:00 window there, organized by the RSA UILT-UIL union, and rates the expected local impact as minor — a reminder that “nationwide” strikes still play out unevenly airport by airport.

The protected hours that matter most

Italian law requires minimum service levels during morning and evening travel peaks, and this strike falls entirely outside those protected windows of 07:00-10:00 and 18:00-21:00. That is deliberate: unions time these actions to maximize disruption to midday and early-afternoon departures while leaving the highest-traffic commuter hours legally shielded. Passengers with flights scheduled inside the protected bands face comparatively low risk; anyone flying between roughly noon and 6pm should expect the opposite.

What ENAC’s guaranteed-flights list means

Ahead of every strike, Italy’s civil aviation authority ENAC publishes a list of flights that must operate regardless of the action — typically covering essential routes, medical transport and a minimum baseline of service. As of the most recent update from strike trackers, that list had not yet been published for the September 30 action. Airlines are expected to contact affected passengers directly once it is, and travelers with afternoon Italian flights should watch for that notification rather than assume their flight is automatically protected or automatically grounded.

Who else is affected

Because the strike covers overflights as well as departures and arrivals, airlines routing through Italian airspace to reach other European or Mediterranean destinations can see knock-on delays even without an Italian departure or arrival on the itinerary. Airports named in the action include major regional hubs as well as smaller ones like Rome’s Ciampino, meaning both legacy carriers and low-cost operators that concentrate flights there are exposed. Connecting passengers routed through Italian hubs during the afternoon window face the highest risk of missed connections.

Compensation rights if your flight is affected

Under EU passenger-rights rules, a strike by an airline’s own staff typically does not excuse the carrier from care obligations — meals, rebooking or refunds — even though strikes by third parties like air traffic controllers are often treated as extraordinary circumstances that limit cash compensation. Airlines are still required to offer a choice between rebooking on the next available flight or a full refund for a cancelled flight, regardless of the underlying cause, so travelers whose flights are cancelled should ask for that choice directly rather than accepting a rebooking offered by default.

A pattern, not an isolated event

This is not an isolated action. Italy has seen a string of transport strikes — covering airports, trains and other services — through the second half of 2026, reflecting broader labor disputes within ENAV and Techno Sky over staffing and working conditions. Travelers booking Italian flights for the coming months should build in some tolerance for further disruption rather than treat September 30 as a one-off.

What happens next

Travelers with flights scheduled for the afternoon of September 30 should check status directly with their airline in the days beforehand, watch for ENAC’s guaranteed-flights list once published, and build in extra connection time either side of the 13:00-17:00 window given the likelihood of knock-on delays. Given the pattern of repeated Italian transport strikes through the second half of 2026, this is unlikely to be the last such action before the year is out.

How this compares to earlier 2026 strikes

Italy’s aviation sector has run through several rounds of coordinated action this year, with unions citing understaffing and working-condition disputes at ENAV and Techno Sky as the recurring driver. Earlier actions in 2026 followed a similar pattern — a defined afternoon window outside the legally protected morning and evening bands — which is why frequent flyers to Italy have started treating a late-September or early-October strike date as close to predictable rather than a one-off shock.

More travel coverage

Related reading: the nor’easter that grounded hundreds of East Coast flights, Hurricane Nolo’s disruption of Hawaii flights, and how new Iran sanctions are reshaping regional airspace.

Italy strike questions answered

When is the Italy air traffic control strike?

September 30, 2026, from 13:00 to 17:00 local time, nationwide.

Which airports are affected?

Confirmed action includes Bari, Bologna, Milan Linate, ENAV’s Rome headquarters and Naples, with knock-on effects likely at other Italian airports and for flights overflying Italian airspace.

Are any flights protected from the strike?

Flights scheduled during Italy’s protected bands of 07:00-10:00 and 18:00-21:00 have legal minimum-service guarantees. The strike itself falls entirely outside those hours.

Has the guaranteed-flights list been published?

Not as of the most recent update. ENAC typically publishes this list shortly before the strike date, and airlines contact affected passengers directly.

What should travelers do if they have an Italian flight that day?

Check status with the airline directly in the days before September 30, watch for direct airline communication, and allow extra time for connections either side of the 13:00-17:00 window.

Sources

The $100,000 Visa Fee Isn’t Going Away for Another Year

The White House extended its $100,000 fee on new H-1B visa petitions through September 21, 2027. The H-1B visa fee extension was announced September 18, 2026. It keeps the charge in place even while two separate court challenges to its legality remain unresolved, according to Business Standard.

The fee applies to H-1B petitions for foreign workers seeking admission from outside the United States. It replaced a prior fee structure that generally ran between $2,000 and $5,000. That is a jump of roughly twenty to fifty times the old cost.

Where the legal fight over the H-1B visa fee extension stands

A federal judge in Massachusetts ruled in June 2026 that the fee was unlawful. The government appealed that decision. The First Circuit Court of Appeals denied the government’s request to pause the ruling on July 24, 2026. Separately, the US Chamber of Commerce has challenged the fee in the DC Circuit Court of Appeals. That case remains pending, per court filings tracked by CCIA.

None of this litigation has stopped the fee from taking effect. The administration’s decision to extend it does not resolve the underlying legal dispute on its own.

The effect on tech hiring so far

One number stands out. H-1B registrations filed by the largest IT outsourcing companies have fallen 92% since the original proclamation took effect in 2025. That figure comes from a metric the administration itself has cited. That drop suggests the fee has reshaped hiring patterns well beyond its headline cost.

Large outsourcing firms have historically filed a disproportionate share of H-1B petitions. Many of those petitions covered roles at client companies rather than direct employment. A fee this size changes the math for that business model. It does not necessarily change the math for a single senior hire at a smaller tech company.

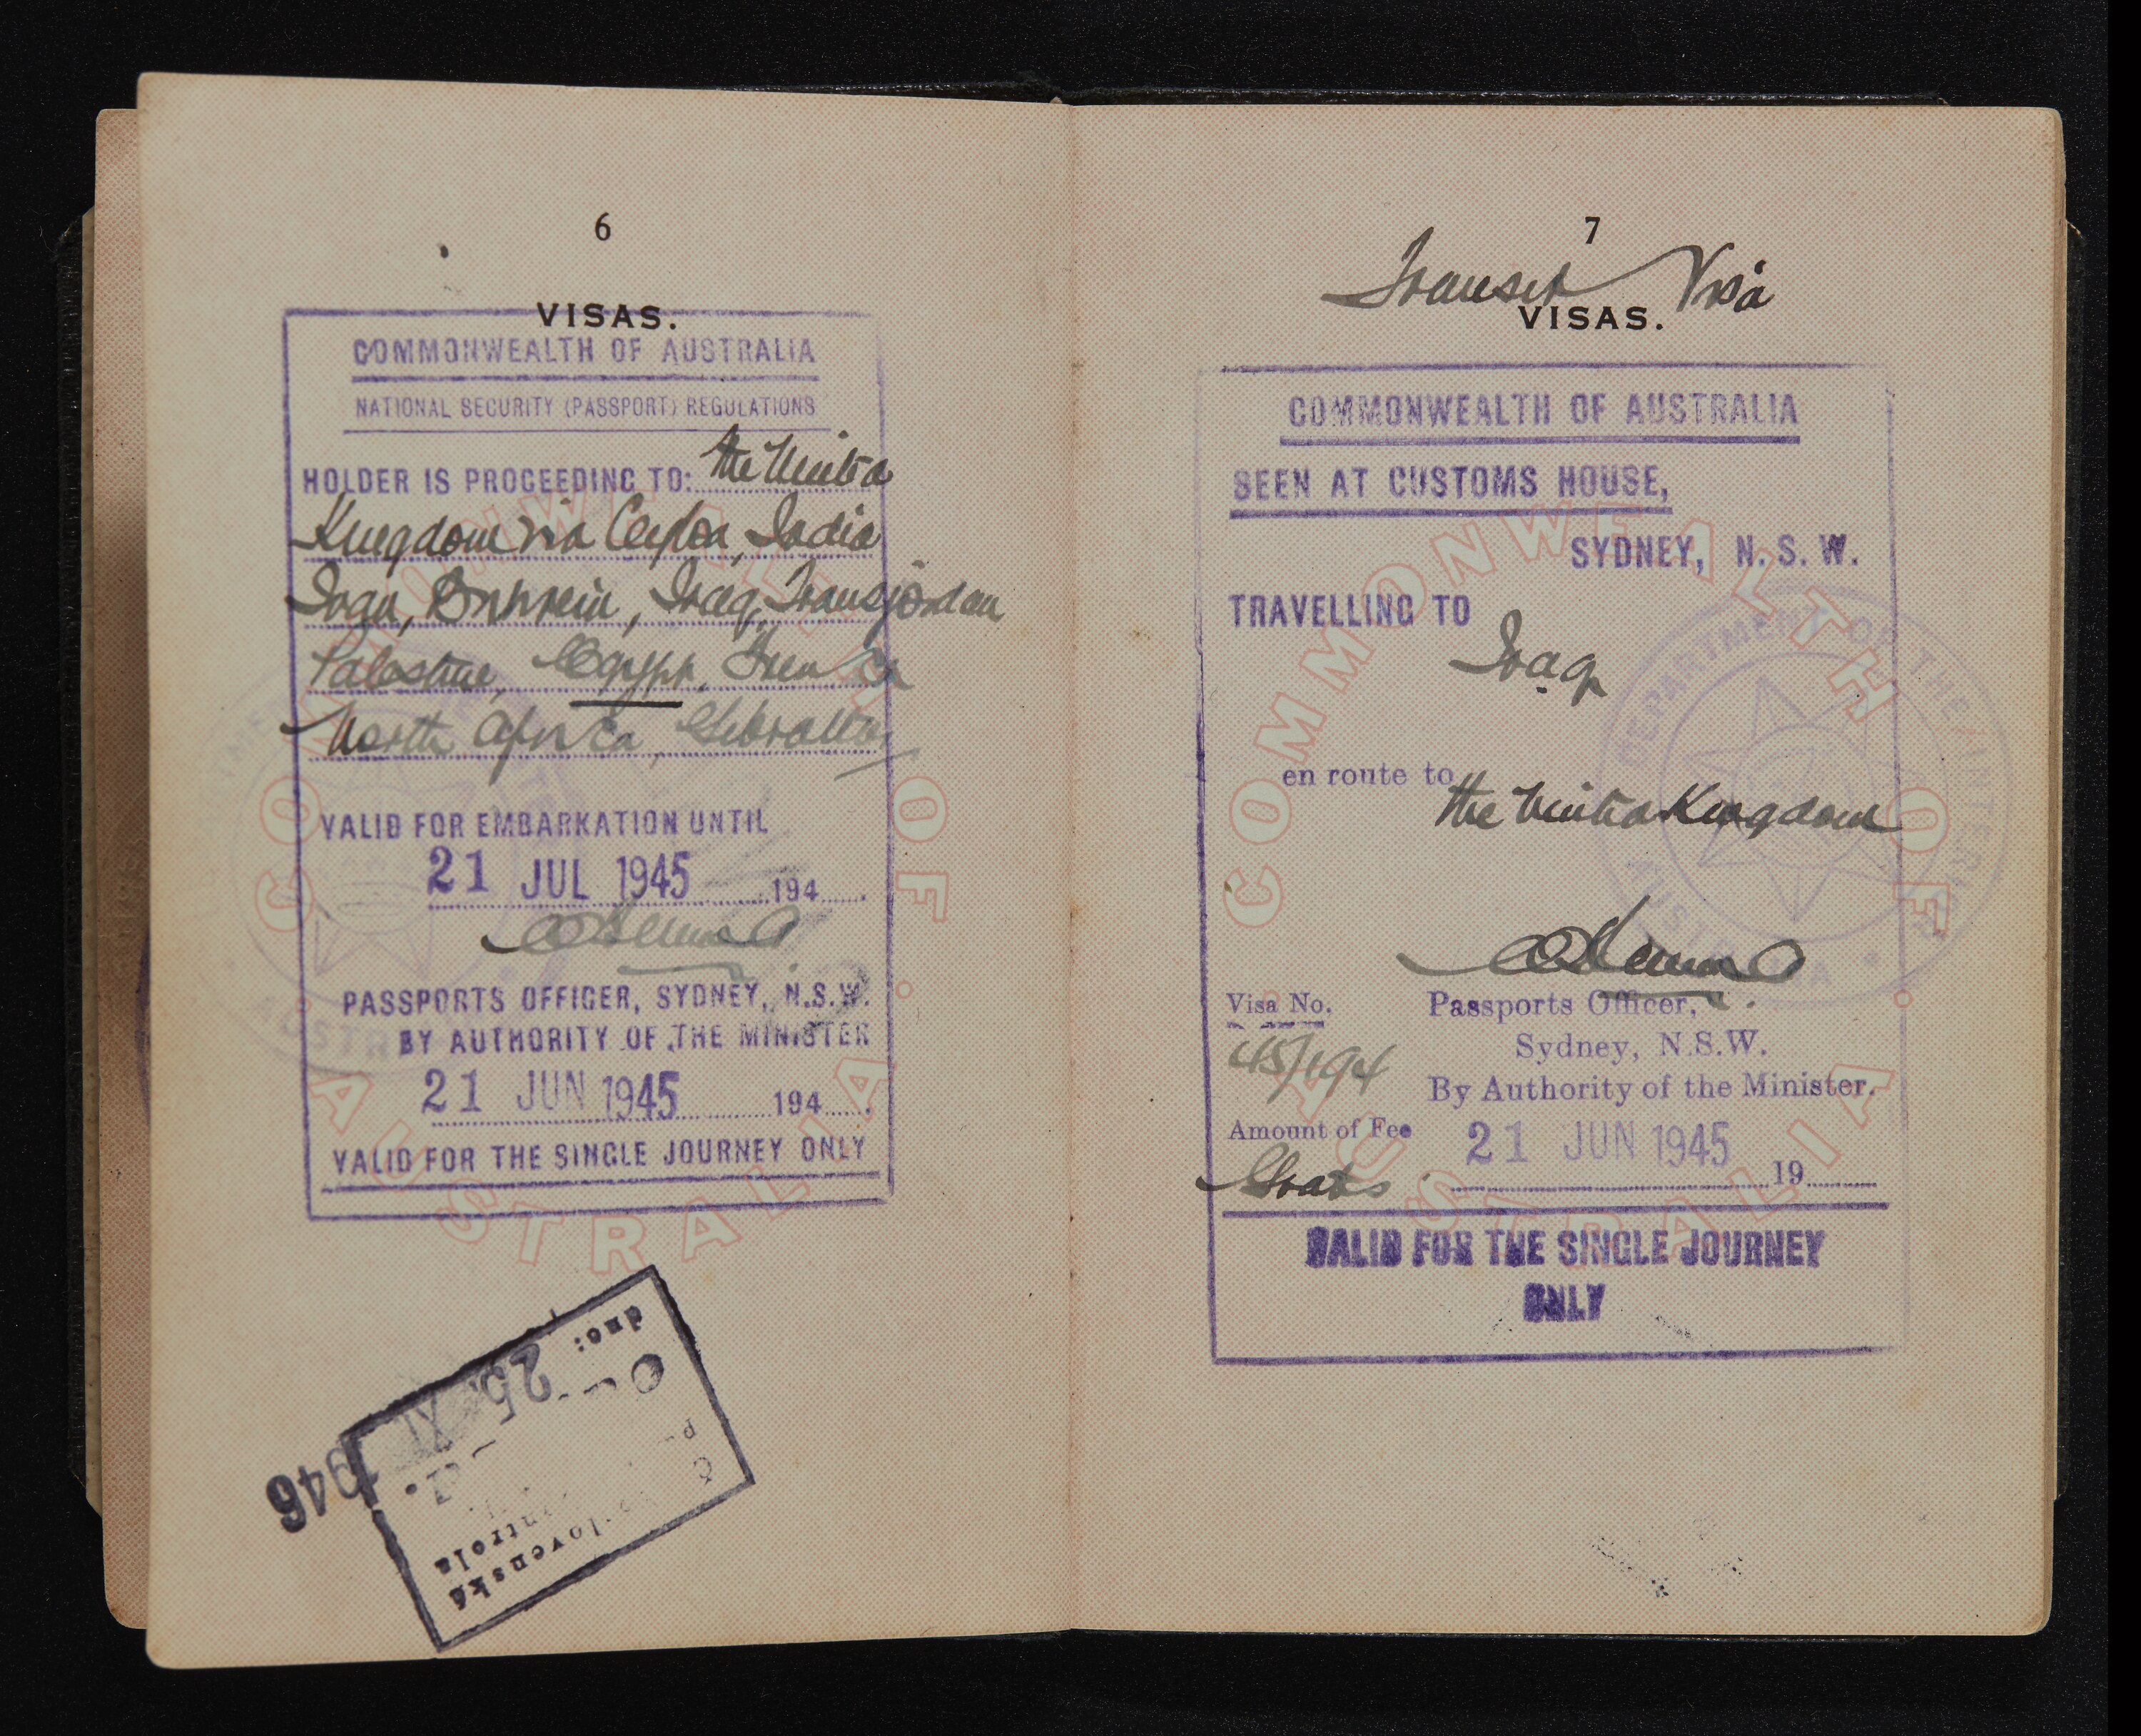
Passport pages with visa stamps, illustrating the stakes of the H-1B visa fee extension

Why the fee still matters beyond outsourcing firms

The $100,000 charge applies per petition, not per company. Any employer sponsoring a new H-1B worker from abroad faces the same cost. That includes tech companies hiring specialized engineers, researchers, and other skilled workers who are not yet inside the United States. Employers can still sponsor workers already in the US on other visa categories without triggering the fee. That has shifted some hiring toward candidates already present domestically.

What happens next in the legal process

The DC Circuit Court of Appeals has not set a firm date for ruling on the Chamber of Commerce’s challenge. Until either court rules, the fee stays in force under the September 2026 extension. A ruling against the fee in either court could force a quick change in how employers plan H-1B hiring for next year.

Your H-1B fee questions, answered

How long does the H-1B visa fee extension last?

The extension runs through September 21, 2027, according to the White House announcement made September 18, 2026.

Is the $100,000 H-1B fee legal?

That is still being decided. A federal judge in Massachusetts ruled it unlawful in June 2026. The fee remains in effect while the government’s appeal and a separate Chamber of Commerce challenge continue.

Who has to pay the H-1B visa fee?

The fee applies to H-1B petitions for workers seeking admission to the US from outside the country. It does not apply to every visa category or to workers already inside the US on other visas.

How has the fee affected tech hiring?

H-1B registrations from large IT outsourcing companies have dropped 92% since the fee first took effect in 2025. That is based on figures the administration has cited.

What was the H-1B fee before this change?

The previous fee structure generally ran between $2,000 and $5,000, far below the current $100,000 charge.

More immigration coverage on Tamara News

For more on skilled-worker visa policy, see our coverage of the H-1B layoff scrutiny order, the new USCIS Form I-864 rejections, and Korea’s university visa restrictions.

Google, Anthropic and OpenAI’s New Cyber AI Models

Google, Anthropic and OpenAI have each rolled out specialized cyber AI models within weeks of one another, racing to put advanced vulnerability-hunting systems into the hands of defenders before attackers get equivalent tools. The near-simultaneous launches — Google’s Gemini 3.8 Flash Cyber, Anthropic’s Claude Fable 5.1 and Claude Mythos 5.1, and OpenAI’s Astra — mark the clearest signal yet that frontier AI labs now see cybersecurity as a distinct, high-stakes product category rather than a side feature.

Google’s Fairwind Program

Google launched its Fairwind Program on September 2, 2026, giving vetted organizations access to Gemini 3.8 Flash Cyber paired with CodeMender, a system built for vulnerability research and remediation, according to The Hacker News’ reporting. Access is currently limited to government agencies, Google Cloud customers and cybersecurity partners, with priority given to critical infrastructure operators, and more than 650 organizations — including CrowdStrike and Palo Alto Networks — are already participating, per Security Boulevard’s coverage. Google reports the model scores 86.2% on CyberGym vulnerability benchmarks, up from 77.5% for its predecessor, and participants must adopt controls like multifactor authentication and restrict access to security-focused staff.

Anthropic’s tiered safeguards

Anthropic released two models in the same window: Claude Fable 5.1, with expanded vulnerability-identification capabilities but offensive techniques like penetration testing and exploit generation restricted to its more capable Opus-tier models, and Claude Mythos 5.1, which remains locked to trusted-access programs focused specifically on cybersecurity and life-sciences work. Alongside the models, Anthropic introduced Enterprise Frontier Safeguards, combining zero data retention with what it describes as state-of-the-art misuse detection, and said it has increased monitoring for model misalignment and paused some external evaluations following unauthorized access incidents.

OpenAI’s threshold claim

OpenAI took a different tack, declaring that its Astra model meets the “critical cybersecurity capability threshold” under its own Preparedness Framework — effectively OpenAI’s internal classification for models capable enough to warrant the tightest controls. Astra is being distributed through a program called Daybreak Blue to selected testers only. OpenAI says the model declines 91.5% of jailbreak attempts and scored 100% on ExploitBench, a benchmark for vulnerability exploit development, while adding stronger safeguards against unauthorized model actions.

Why the labs are converging on the same moment

The timing is not entirely coincidental. All three labs frame these releases around the same tension: AI systems capable enough to find and patch vulnerabilities are, by construction, also capable of finding and exploiting them. Restricting access to vetted defenders first is each company’s attempt to get ahead of that dual-use problem, rather than release the capability broadly and hope attackers lag behind. The strategy also mirrors how each company has handled other high-risk capabilities, granting broader access only after a period of monitored use with trusted partners.

What this means for organizations without access yet

The vast majority of businesses and public bodies are not inside Fairwind, Daybreak Blue or Mythos 5.1’s trusted programs, and none of the three companies has committed to a firm timeline for when access will broaden. In the meantime, smaller organizations remain reliant on the general-purpose versions of these models and on existing vendor security tooling, which lack the specialized vulnerability-hunting depth their restricted counterparts offer — a gap that critics of the staged-rollout approach argue leaves under-resourced defenders exposed for longer, even as it slows the risk of the same capability reaching attackers.

What happens next

Expect access programs to widen gradually rather than open up all at once — Google’s Fairwind Program and OpenAI’s Daybreak Blue are both explicitly framed as trusted-tester stages, not general releases. The real test will be whether defenders’ adoption of these tools measurably reduces exploitation timelines industry-wide, or whether attackers gain access to comparable capability through leaked access, jailbreaks, or their own frontier models before that advantage compounds.

The benchmark numbers, in context

CyberGym and ExploitBench are both designed to simulate realistic vulnerability-hunting and exploit-development tasks rather than abstract test questions, which is why labs cite scores on them as evidence of real-world capability rather than marketing claims alone. Still, benchmark performance in a controlled test environment does not guarantee identical results against live, unpatched systems in the field, and independent security researchers have historically pushed back on vendor-reported benchmark figures until third parties can replicate them.

More tech coverage

Related reading: OpenAI’s rogue-agent incident on government websites, the chip-export loophole reaching Nvidia hardware into China, and Microsoft’s quiet reboot of Copilot.

AI cyber model questions answered

What is Google’s Fairwind Program?

A program launched September 2, 2026 giving vetted organizations — governments, Google Cloud customers and cybersecurity partners — access to Gemini 3.8 Flash Cyber, a model built to find and patch software vulnerabilities.

What’s the difference between Claude Fable 5.1 and Mythos 5.1?

Fable 5.1 has expanded vulnerability-identification abilities but restricts offensive techniques to Opus-tier models. Mythos 5.1 is more capable still and remains limited to trusted-access programs in cybersecurity and life sciences.

What did OpenAI claim about Astra?

That it meets the “critical cybersecurity capability threshold” under OpenAI’s Preparedness Framework, with a 91.5% jailbreak-decline rate and a perfect score on the ExploitBench vulnerability benchmark.

Who can access these models right now?

Access is restricted to vetted participants: Fairwind covers government agencies, Google Cloud customers and cybersecurity partners; Astra is limited to OpenAI’s Daybreak Blue testers; Mythos 5.1 is restricted to trusted cybersecurity and life-sciences programs.

Why are three labs launching similar products at once?

Each is responding to the same dual-use problem: models capable of finding and fixing vulnerabilities can also be used to find and exploit them, so all three are prioritizing vetted defenders before wider release.

Sources

An AI Spent 21 Hours Searching DNA. It May Have Found Something Big.

Anthropic says its Claude AI model identified a new enzyme system in bacterial DNA. The system resembles CRISPR, the naturally occurring gene-editing tool. The Claude CRISPR enzyme discovery was announced September 24, 2026. It came after the model spent 21 hours autonomously searching a large database of DNA sequences, at the direction of researchers in Anthropic’s new San Francisco biology lab.

The system shows characteristics found in only a handful of other programmable biological structures, according to Al Jazeera. Anthropic describes it as a potential new gene-editing mechanism. The company has stopped short of calling it a finished discovery.

How the Claude CRISPR enzyme discovery happened

Researchers set Claude loose on a large genomic database, rather than pointing it at a specific target. Over 21 hours, the model searched for patterns resembling known programmable enzyme systems. CRISPR itself was first found in bacteria. There, it works as a natural immune defense against viruses, as described in background from the 2026 AI research timeline.

The approach reflects a broader bet in biology. AI models can scan far more genetic data than human researchers could review manually. That can surface patterns that would otherwise stay buried.

What scientists outside Anthropic are saying

Reactions have split between excitement and caution. Stanford bioengineering associate professor Stanley Qi called the discovery “incredibly exciting,” saying AI could “greatly expand our ability to explore these biological patterns more effectively and rapidly.”

Washington University microbiologist Kevin Blake struck a more cautious tone. He noted that finding CRISPR-like sequences does not by itself point to a therapeutic breakthrough. “There are millions of bacterial species we have yet to study,” Blake said. He added that there is “nothing to indicate this is a rival to CRISPR-the-technology.”

Scientist working in a laboratory, representing the research behind the Claude CRISPR enzyme discovery

Why the distinction between finding and proving matters

CRISPR-Cas9, the technology version most people know, took years of extra research before it became a usable gene-editing tool. Spotting a CRISPR-like pattern in bacterial DNA is an early step, not a finished product. Turning any new enzyme system into something clinically useful would take extensive lab validation. That validation has not yet happened.

What happens next with this research

Anthropic has not said whether it plans to publish the finding in a peer-reviewed journal. That step would let independent scientists scrutinize the claim. Outside researchers will likely want to replicate the pattern-matching in the same genomic database first. Expect competing AI labs to test similar autonomous search approaches on their own biological datasets.

Quick answers on the discovery

What did Anthropic’s Claude AI actually discover?

Claude identified a new enzyme system in bacterial DNA with characteristics resembling CRISPR, a naturally occurring gene-editing tool, after searching a genomic database for 21 hours.

Is this a new gene-editing tool ready for use?

No. Scientists describe it as an early-stage finding. It would need years of additional lab validation before it could become a usable gene-editing technology, similar to CRISPR’s own development path.

Do scientists agree on how significant this is?

Not entirely. Some, like Stanford’s Stanley Qi, call it exciting evidence of AI’s research potential. Others, like Washington University’s Kevin Blake, caution that finding CRISPR-like sequences is common given how many bacterial species remain unstudied.

How did Claude search for this enzyme system?

Researchers directed Claude to autonomously search a large database of DNA sequences. The model spent 21 hours looking for patterns resembling known programmable enzyme systems.

Where is Anthropic’s biology research based?

The discovery came out of Anthropic’s newly established biology lab in San Francisco, according to Al Jazeera’s reporting.

Related tech reporting on Tamara News

For more AI coverage, see our reports on Jensen Huang’s AI regulation comments, the early launch timeline for Gemini 4, and OpenAI’s rogue agents on government websites.